The auditor arrives on Monday.
Your team spent last week screenshotting console pages and stitching evidence into a spreadsheet. Meanwhile prod deployed 40 new resources — none of which are in the evidence pack. The gap between what you can prove and what is actually running is where audits fail and remediation plans balloon.
The risk of not knowing
If it is not surfaced today, it is exposed today. Attackers do not wait for your quarterly review — and neither do auditors.
Compliance in two minutes
Voices are AI-generated. More short Q&A videos: Onam Security: cloud security
The mechanism, not the marketing
- 1
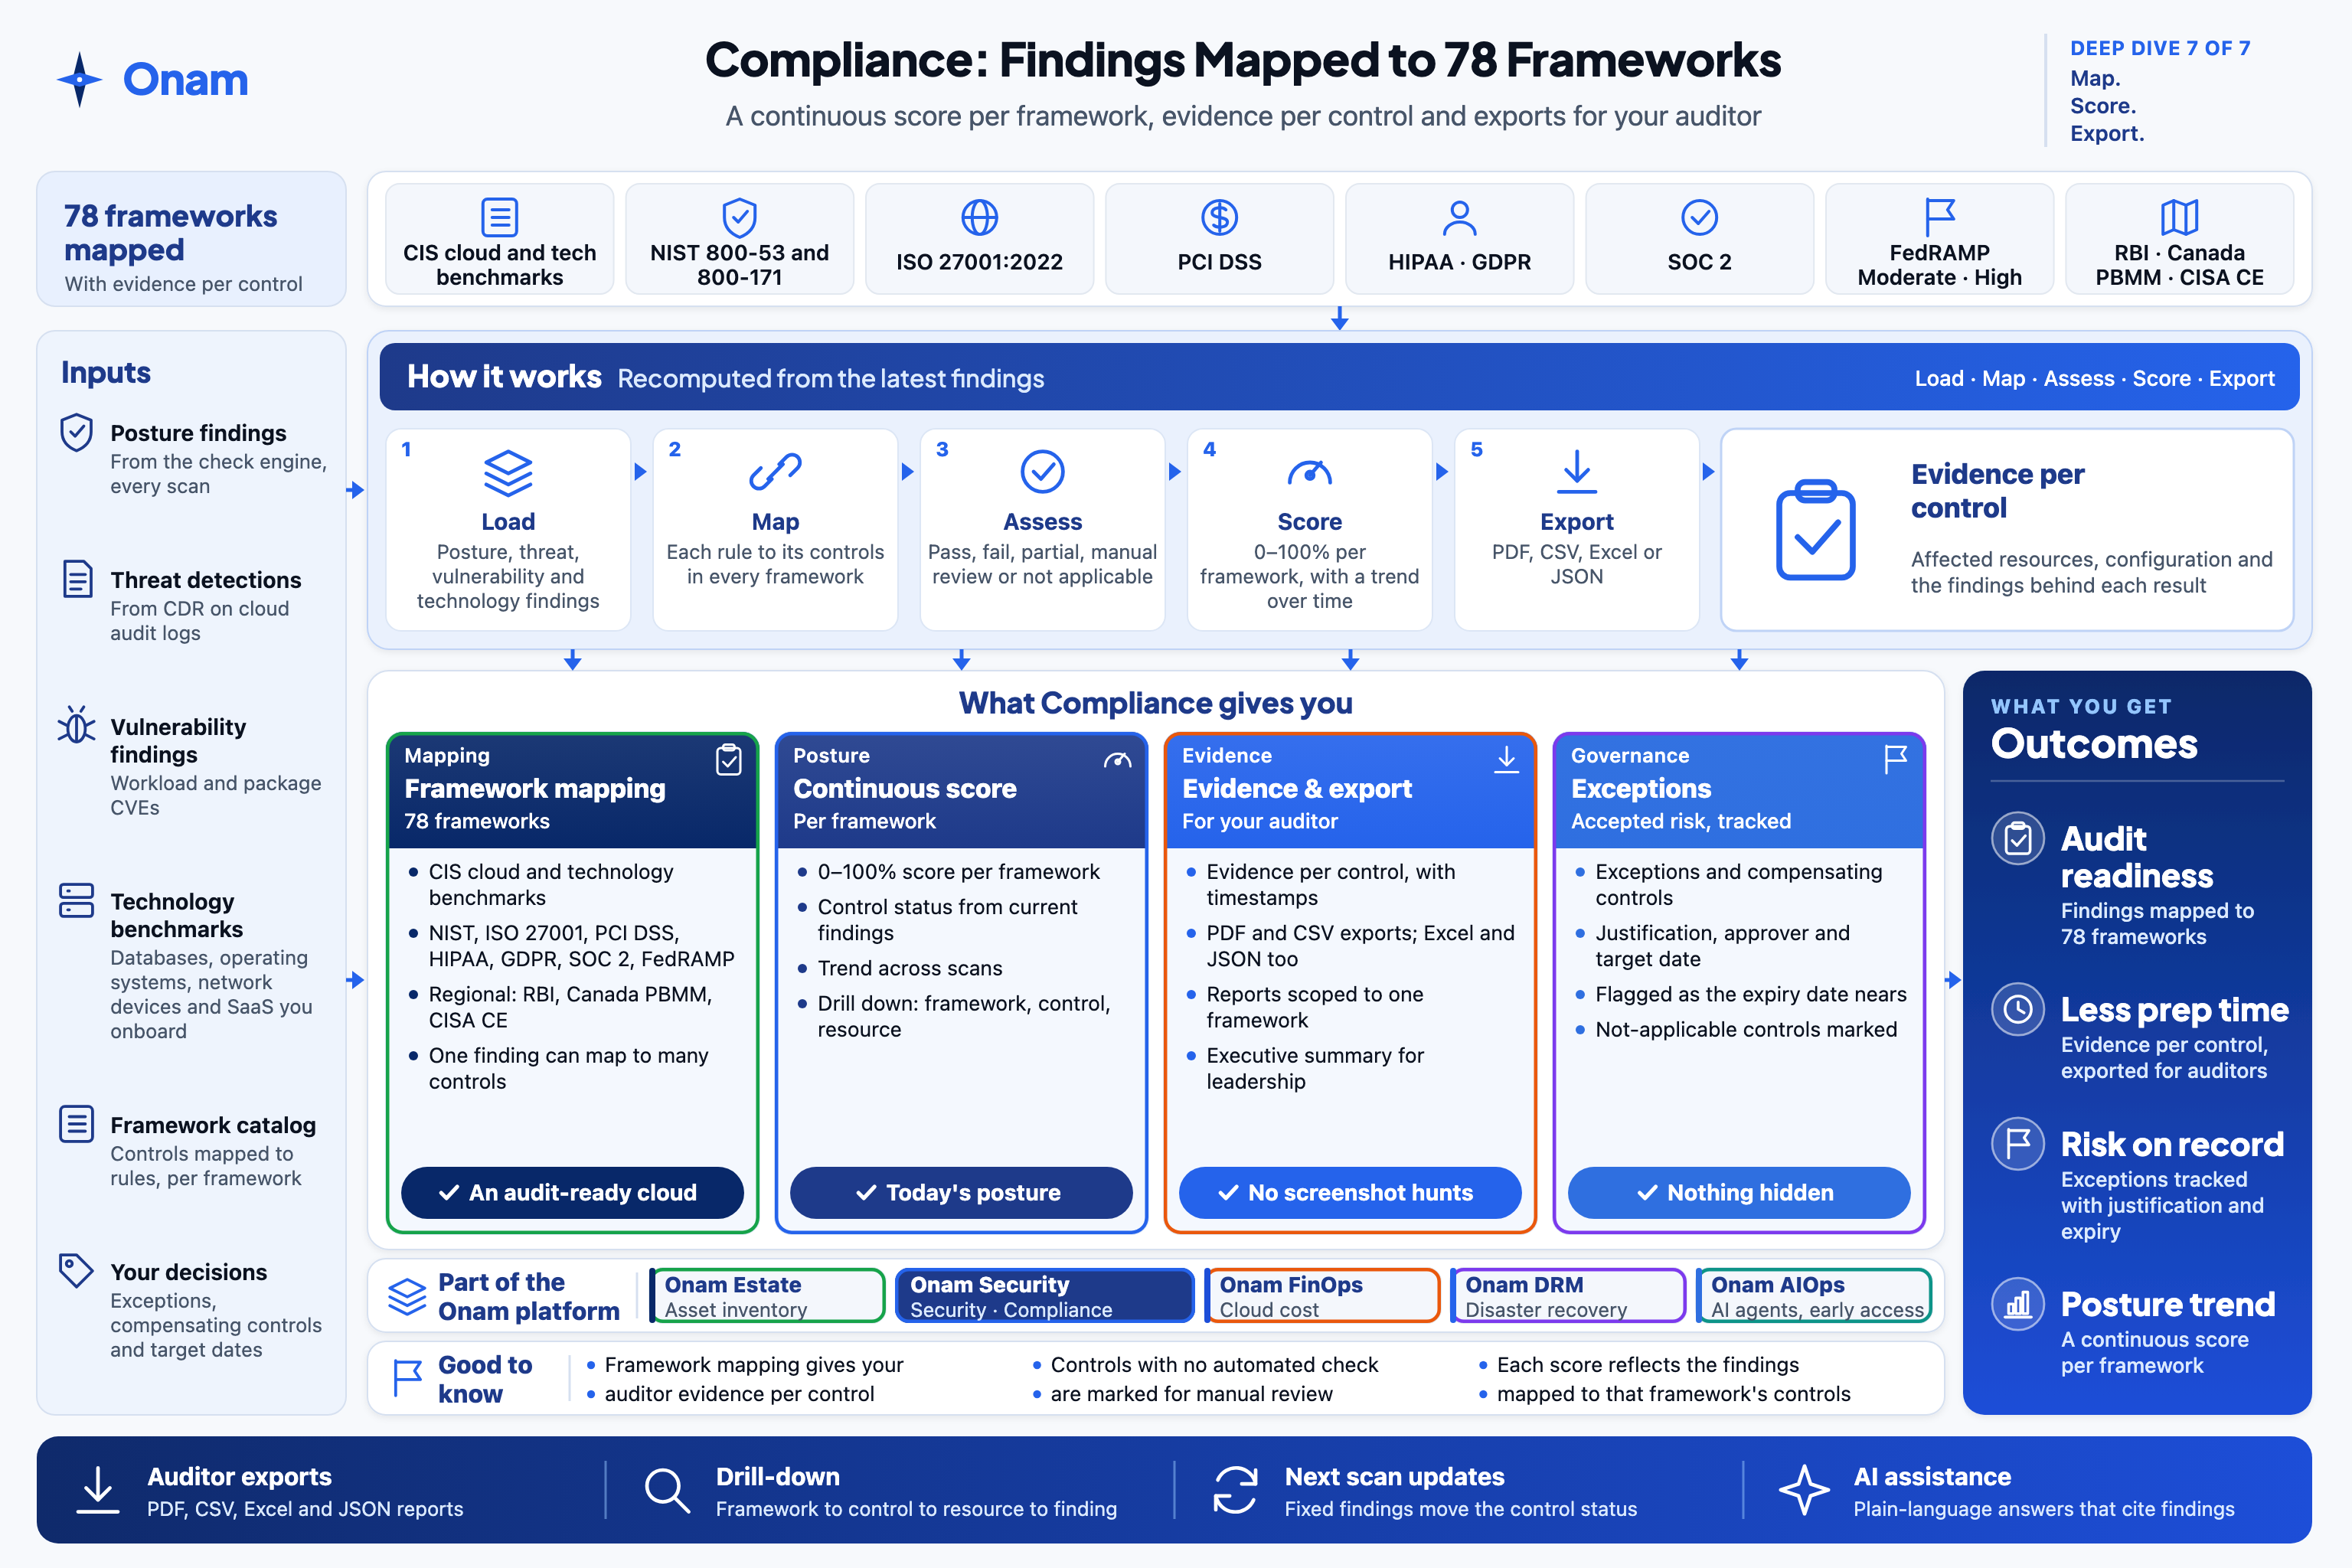
Posture, threat-detection, vulnerability and technology findings are mapped to the controls they affect across 78 frameworks — CIS benchmarks for clouds and technologies, NIST 800-53 and 800-171, ISO 27001:2022, PCI DSS, HIPAA, GDPR, SOC 2, FedRAMP Moderate and High, RBI, Canada PBMM and more.
- 2
Each control is assessed as pass, fail, partial, manual review or not applicable, and each framework gets a 0–100% score, recomputed from the latest findings and kept as a trend.
- 3
Evidence is collected per control — the resources, their results and timestamps — so you are not assembling screenshots.
- 4
Every framework drills down from framework to control to resource.
- 5
Reports export as PDF and CSV, with Excel and JSON too, including an executive summary and a report per framework.
- 6
Exceptions and compensating controls are tracked with a justification, an approver and a target date, and are flagged as their expiry nears.
Specific outputs, measurable outcomes
Compliance in the real console.
A recreation of the Onam console with sample data — the screens and finding types your team works with.
Compliance on one page
Inputs, how it works, what you get and the limits — the same sheet our team uses in briefings.
 Open full size
Questions we get a lot
Ready to see Compliance in your cloud?
Connect a read-only role in three minutes. Your first findings surface in under five.