What is our overall cloud security posture, in one number?
CNAPP: one posture score built from seven separately scored pillars.
CNAPP is the unified view across what Onam runs: posture, threat detection and identity, workloads, data, network, threat and code. Each is scored as a pillar, and the pillars roll up into one posture score that a board can read and an engineer can drill into.
- posture rules
- 9,853
- cloud providers
- 7
- cloud services
- 549
- compliance frameworks
- 78
Every security tool reports its own number.
Posture says 74. The vulnerability scanner reports thousands of open CVEs. The compliance tool says 88% CIS. The identity tool lists hundreds of over-privileged roles. None of them are wrong and none of them combine, so the answer to 'are we getting better' becomes a quarterly slide someone assembles by hand from four exports.
CNAPP in two minutes
Voices are AI-generated. More short Q&A videos: Onam Security: cloud security
How CNAPP works
- 01
Seven pillars are scored on a common 0–100 scale: posture (CSPM), threat detection with IAM posture (CDR), workloads (CWPP), data (DSPM), network, threat, and code (AppSec).
- 02
Each pillar's score comes from its own engine. For posture, it is the share of checks that pass.
- 03
The pillars are combined with fixed weights into one overall score with a risk band: low, medium, high or critical. A pillar with no data is left out and the remaining weights are rebalanced.
- 04
Each overall score is stored, so the trend over time shows whether posture is improving.
- 05
Behind the pillars sits one findings model: findings from every engine land in the same place, and severity is raised for a finding on an attack path that is internet-exposed, on a high-value asset, on a likely-exploited CVE or touched by an active threat actor, with a fix-by date per finding.
What you see in the console
- One posture score with a risk band, trended over time
- Seven pillar scores
- posture, threat detection and IAM, workloads, data, network, threat, code
- Fixed pillar weights, rebalanced when a pillar has no data
- Drill-down from pillar to the findings behind it
- Context-raised severity and a fix-by date per finding
CNAPP in the real console.
A recreation of the Onam console with sample data — the screens and finding types your team works with.
CNAPP on one page
Inputs, how it works, what you get and the limits — the same sheet our team uses in briefings.
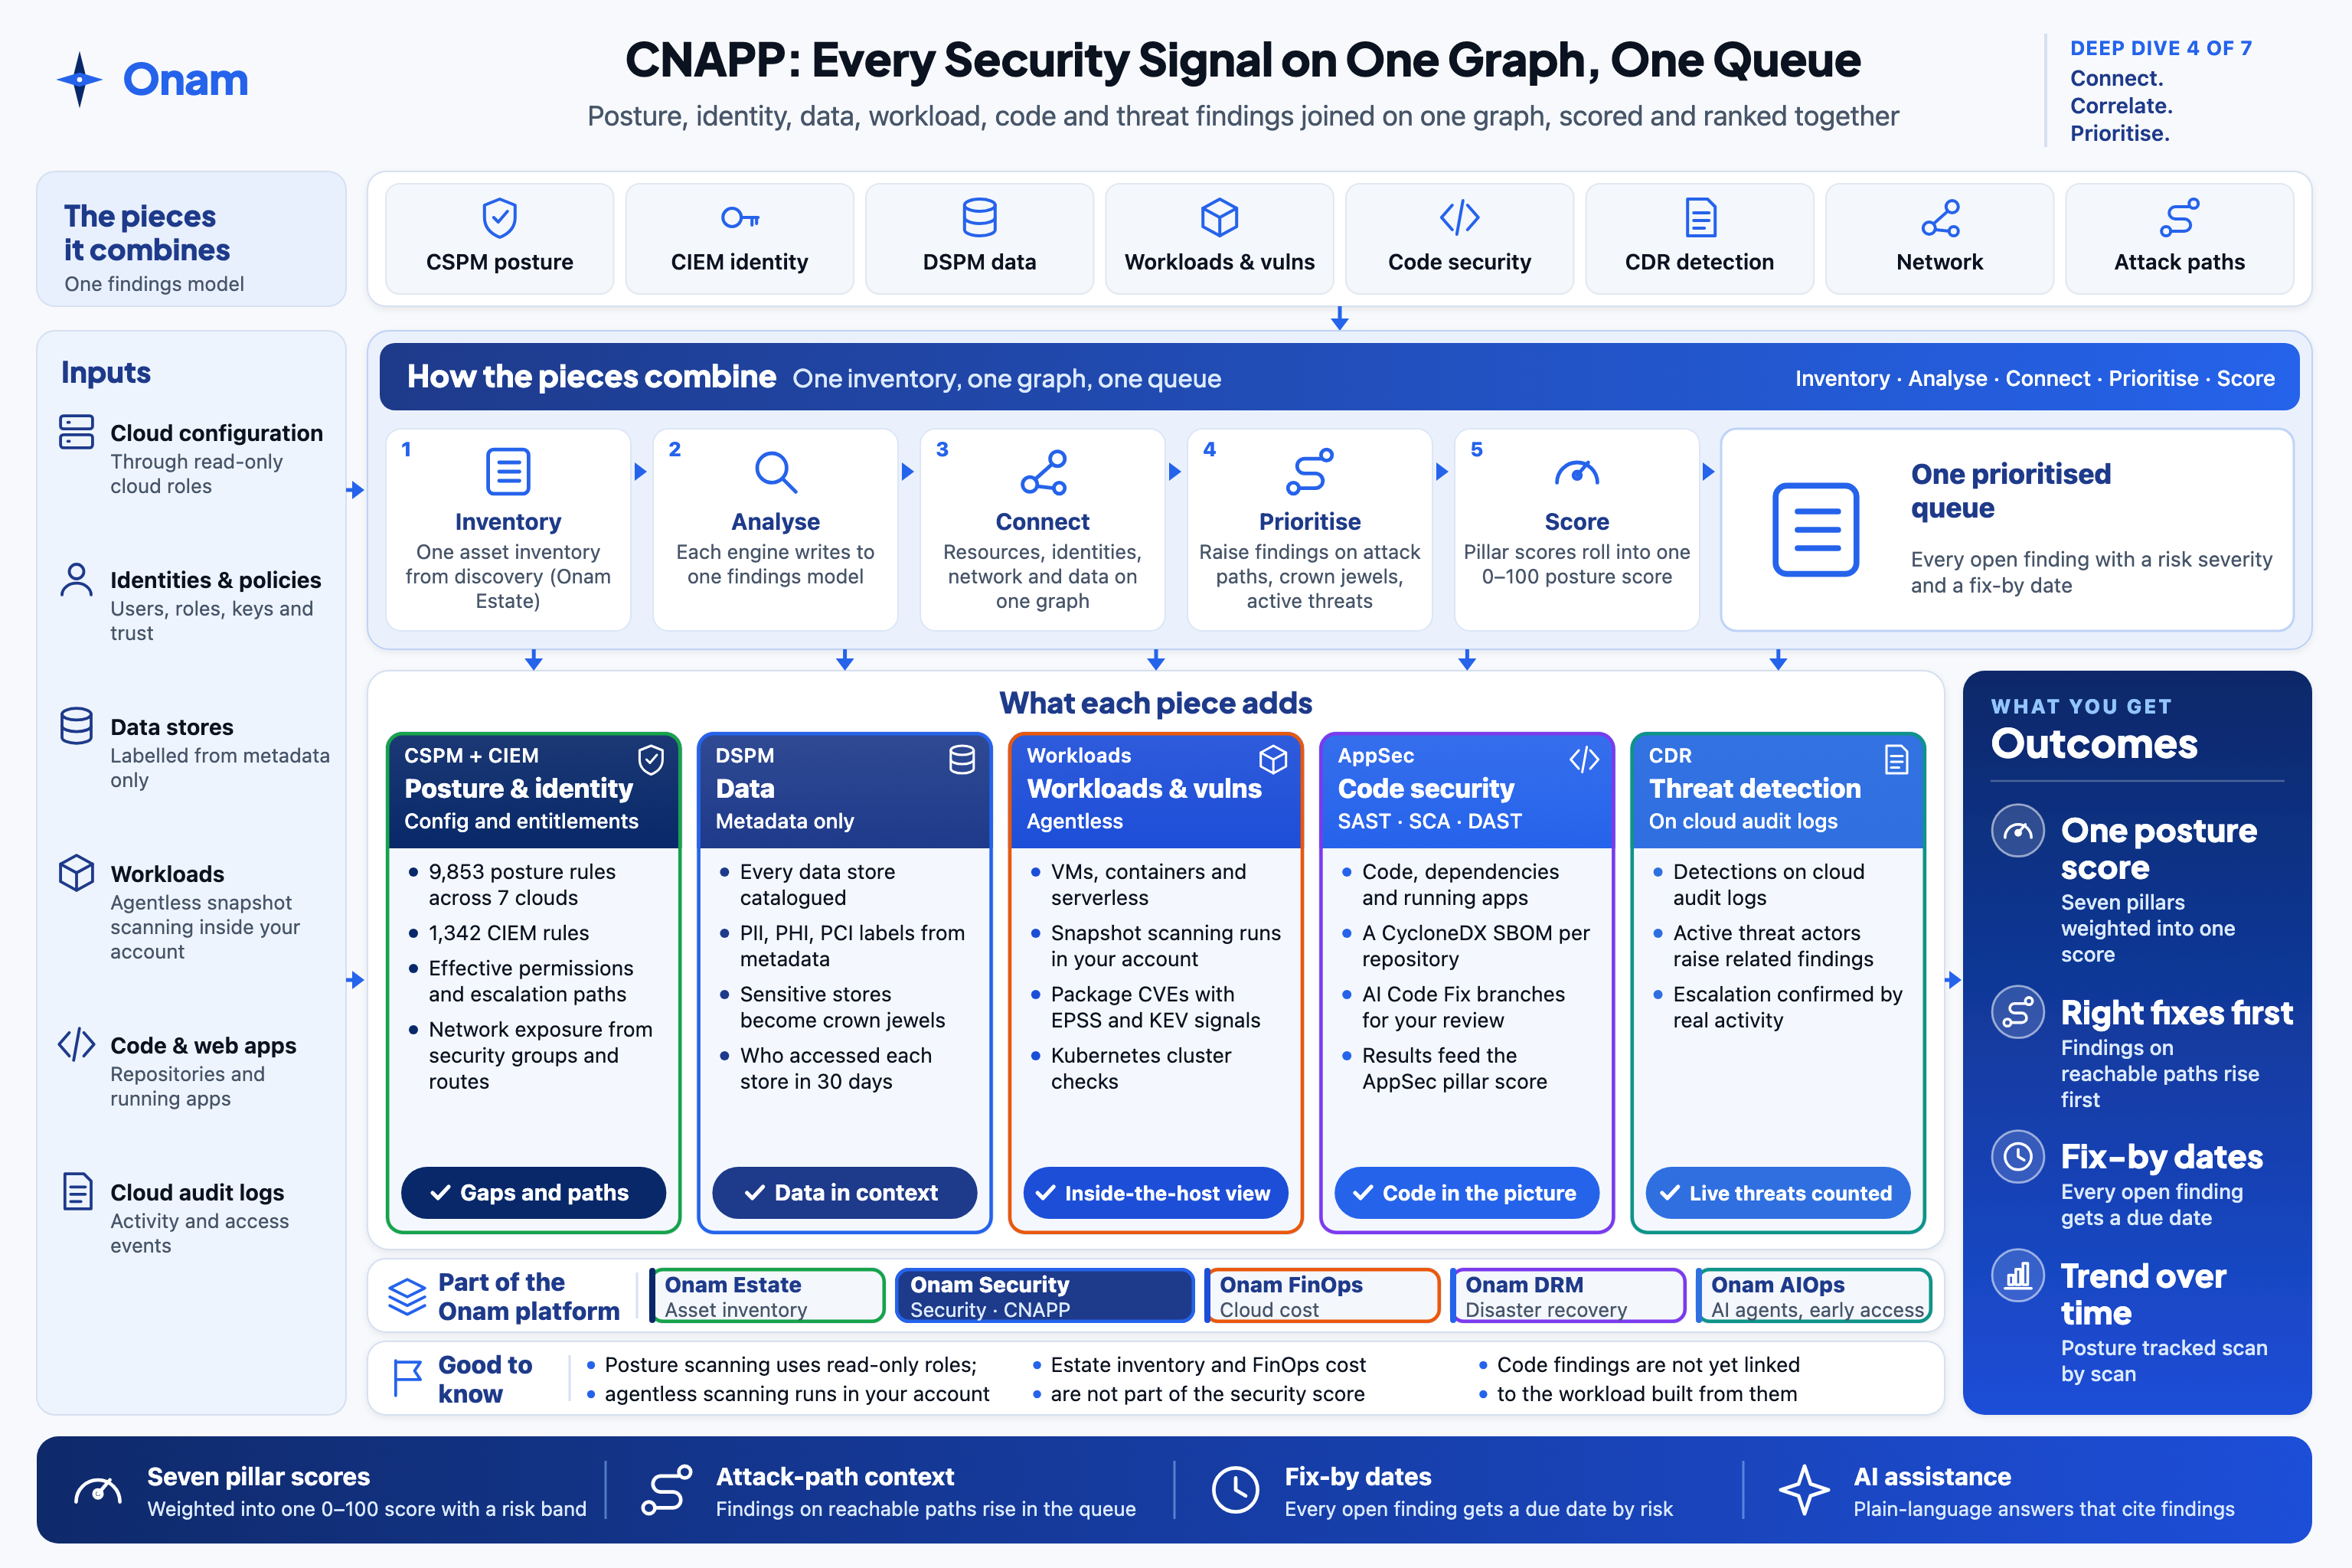 Open full size
Questions we get a lot
See CNAPP on your own cloud
Book a 30-minute demo. We walk through it on sample data, or on one of your accounts if you want to connect it.