A medium-severity SSRF on an EC2 instance.
A dormant IAM role with S3 write. A subnet with an over-permissive NACL. Three findings, three teams, three sprints. Individually they look like noise; chained together they are a route to your customer database. A flat finding list shows them separately — an attacker sees the path.
The risk of not knowing
If it is not surfaced today, it is exposed today. Attackers do not wait for your quarterly review — and neither do auditors.
Attack Path Analysis in two minutes
Voices are AI-generated. More short Q&A videos: Onam Security: cloud security
The mechanism, not the marketing
- 1
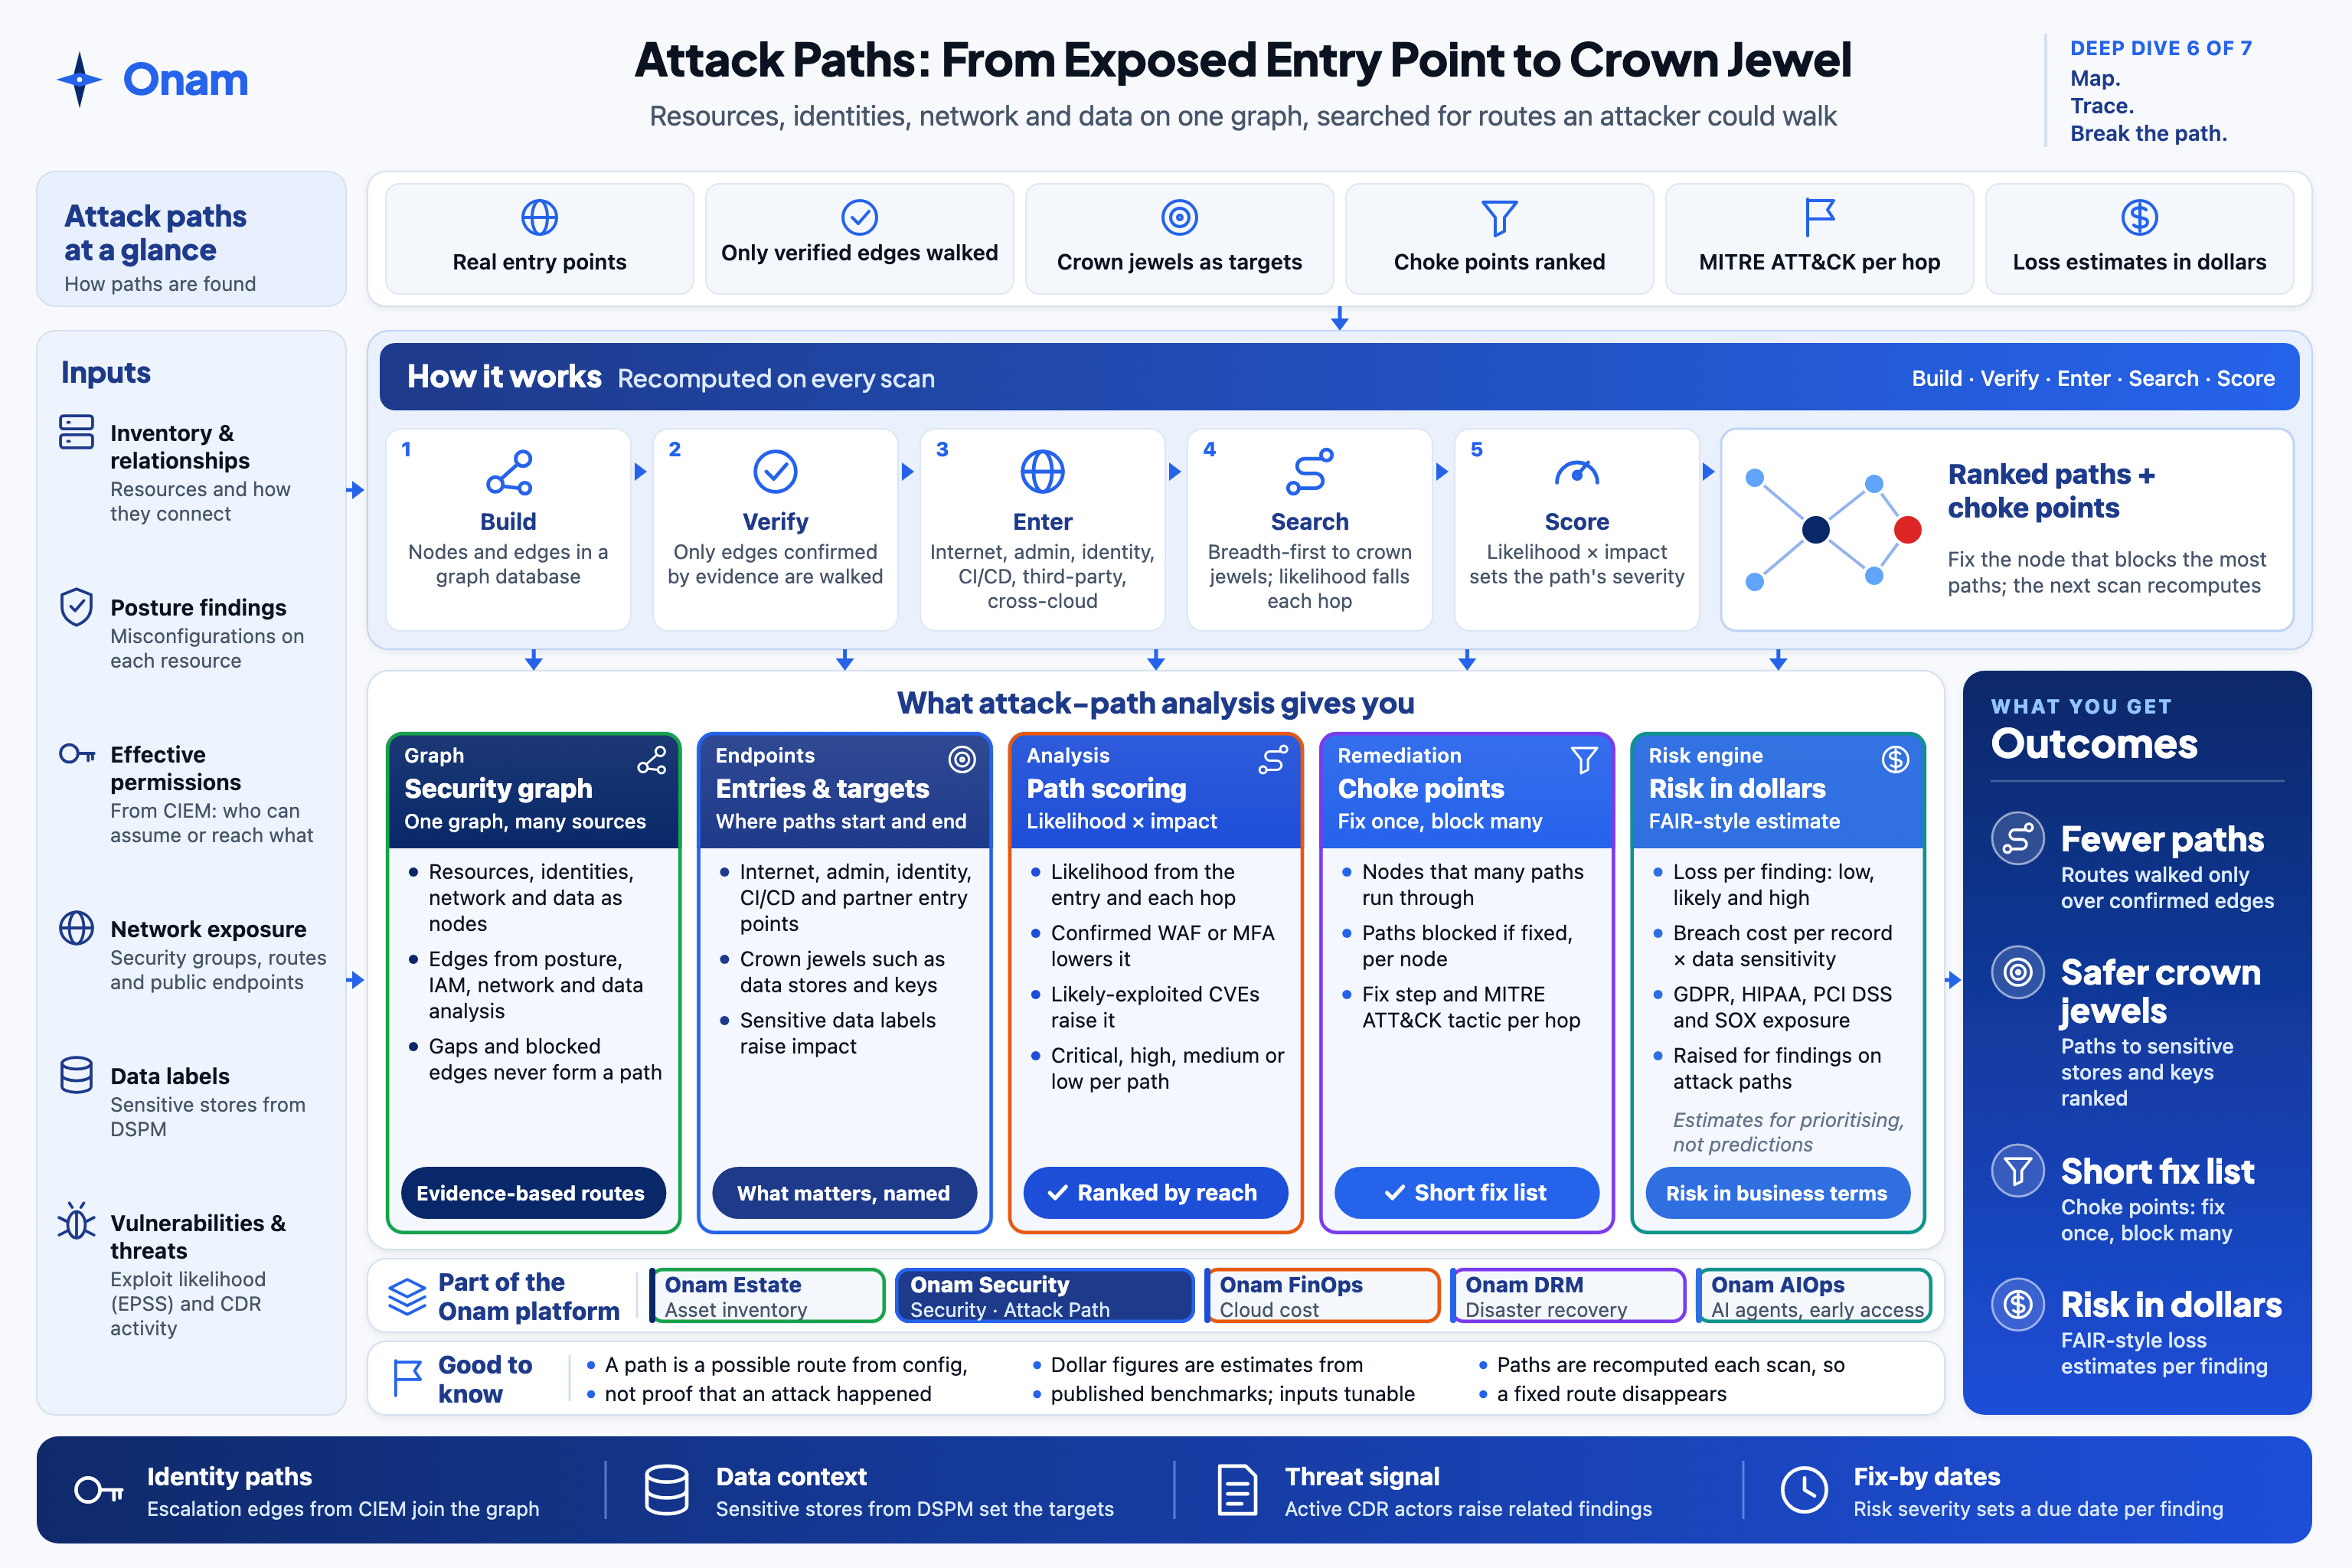
Onam loads your resources into a graph database. Edges come from evidence: IAM policies, network exposure and security-group rules, data access, and movement seen by threat detection.
- 2
Each edge is marked confirmed, blocked or gap. Only edges confirmed by evidence are walked, so a route that a security group or a policy actually blocks does not become a path.
- 3
Paths start from entry points — the internet, admin and other identities, CI/CD, third parties, other clouds — and are searched breadth-first toward crown jewels such as data stores and encryption keys. Likelihood decays with every hop.
- 4
Each path is scored as likelihood times impact and given a severity. Controls such as a WAF or MFA lower the score; a hop with a high-EPSS vulnerability raises it.
- 5
Choke points are the resources many paths share. For each one, Onam shows how many paths would be blocked if you fixed it.
- 6
Every hop carries its MITRE ATT&CK tactic and technique and a remediation step, and the whole graph is rebuilt on every scan, so a fixed route is simply gone at the next one.
Specific outputs, measurable outcomes
Attack Path Analysis in the real console.
A recreation of the Onam console with sample data — the screens and finding types your team works with.
Attack paths on one page
Inputs, how it works, what you get and the limits — the same sheet our team uses in briefings.
 Open full size
Questions we get a lot
Ready to see Attack Path Analysis in your cloud?
Connect a read-only role in three minutes. Your first findings surface in under five.